Learn more">
Skip to navigation
/n <img src=https://elevenlabs.io/"file:assets/images/entra-saml-verify-domain.png/" alt=\"ElevenLabs bulk domain verification dialog\" />\n </Frame>\n </Step>\n\n {\" \"}\n\n <Step title=\"Select SAML as the SSO provider\">\n In **SSO Provider**, select **SAML**. Copy the **Service Provider Entity Id** and **Redirect URL**\n values. You will use these values in Microsoft Entra.\n </Step>\n\n <Step title=\"Create a Microsoft Entra enterprise application\">\n In the Microsoft Entra admin center, open your directory **Overview**, then click **Add** >\n **Enterprise application**.\n\n <Frame background=https://elevenlabs.io/"subtle/">/n <img src=https://elevenlabs.io/"file:assets/images/entra-saml-new-application.png/" alt=\"Microsoft Entra Overview Add menu with Enterprise application selected\" />\n </Frame>\n\n On **Browse Microsoft Entra App Gallery**, click **Create your own application**.\n\n <Frame background=https://elevenlabs.io/"subtle/">/n <img src=https://elevenlabs.io/"file:assets/images/entra-saml-create-application.png/" alt=\"Microsoft Entra App Gallery with Create your own application\" />\n </Frame>\n </Step>\n\n <Step title=\"Name the application\">\n Enter a name (for example, `ElevenLabs`), select **Integrate any other application you don't find\n in the gallery (Non-gallery)**, then click **Create**.\n\n <Frame background=https://elevenlabs.io/"subtle/">/n <img src=https://elevenlabs.io/"file:assets/images/entra-saml-name-application.png/" alt=\"Microsoft Entra Create your own application panel with a non-gallery app\" />\n </Frame>\n </Step>\n\n <Step title=\"Start single sign-on setup\">\n On the application **Overview**, under **Getting Started**, select **Set up single sign on** >\n **Get started**.\n\n <Frame background=https://elevenlabs.io/"subtle/">/n <img src=https://elevenlabs.io/"file:assets/images/entra-saml-set-up-sso.png/" alt=\"Microsoft Entra enterprise application Getting Started with Set up single sign on\" />\n </Frame>\n\n Select **SAML** as the single sign-on method.\n\n <Frame background=https://elevenlabs.io/"subtle/">/n <img src=https://elevenlabs.io/"file:assets/images/entra-saml-select-saml.png/" alt=\"Microsoft Entra Select a single sign-on method with SAML\" />\n </Frame>\n </Step>\n\n <Step title=\"Configure basic SAML settings\">\n In **Basic SAML Configuration**, configure the app with the values from ElevenLabs:\n\n * Set **Identifier (Entity ID)** to the ElevenLabs **Service Provider Entity Id**.\n * Set **Reply URL (Assertion Consumer Service URL)** to the ElevenLabs **Redirect URL**.\n * Leave **Sign on URL** blank. ElevenLabs uses SP-initiated SSO.\n\n Click **Save**.\n\n <Frame background=https://elevenlabs.io/"subtle/">/n <img src=https://elevenlabs.io/"file:assets/images/entra-saml-basic-configuration.png/" alt=\"Microsoft Entra Basic SAML Configuration with Identifier and Reply URL\" />\n </Frame>\n\n <Note>\n For [data residency](/docs/overview/administration/data-residency) environments, use\n `https://<region>.residency.elevenlabs.io/__/auth/handler` as the Reply URL, replacing\n `<region>` with your region code.\n </Note>\n </Step>\n\n <Step title=\"Configure the Name ID claim\">\n In **Attributes & Claims**, edit the **Unique User Identifier (Name ID)** claim:\n\n * Set **Name identifier format** to **Email address**.\n * Set **Source** to **Attribute**.\n * Set **Source attribute** to the field that contains the email address for all users. This is\n usually `user.mail`, but may be `user.userprincipalname`.\n\n Click **Save**.\n\n <Note>\n Choose the attribute that holds an email address for every user. If `user.mail` is not populated\n for all of your users, use `user.userprincipalname` instead.\n </Note>\n\n <Frame background=https://elevenlabs.io/"subtle/">/n <img src=https://elevenlabs.io/"file:assets/images/entra-saml-attributes-claims.png/" alt=\"Microsoft Entra Manage claim with Email address format and user.mail source attribute\" />\n </Frame>\n </Step>\n\n <Step title=\"Download the signing certificate\">\n In **SAML Certificates**, next to **Certificate (Base64)**, click **Download**. Open the\n downloaded file in a text editor.\n\n <Frame background=https://elevenlabs.io/"subtle/">/n <img src=https://elevenlabs.io/"file:assets/images/entra-saml-download-certificate.png/" alt=\"Microsoft Entra SAML Certificates with Certificate Base64 download\" />\n </Frame>\n </Step>\n\n <Step title=\"Assign users or groups\">\n Open the app's **Users and groups**, then assign the users or groups that should be able to sign\n in to ElevenLabs.\n\n <Frame background=https://elevenlabs.io/"subtle/">/n <img src=https://elevenlabs.io/"file:assets/images/entra-saml-assign-users.png/" alt=\"Microsoft Entra Add Assignment users list\" />\n </Frame>\n </Step>\n\n <Step title=\"Add the Entra certificate to ElevenLabs\">\n In ElevenLabs, click **Add Certificate**. Paste the full PEM certificate from the Base64 file,\n including `-----BEGIN CERTIFICATE-----` and `-----END CERTIFICATE-----`, then click **Add**.\n\n <Frame background=https://elevenlabs.io/"subtle/">/n <img src=https://elevenlabs.io/"file:assets/images/entra-saml-add-certificate.png/" alt=\"ElevenLabs Add X509 Certificate dialog\" />\n </Frame>\n </Step>\n\n <Step title=\"Copy Entra identity provider values into ElevenLabs\">\n In the Microsoft Entra **Set up** section, copy the identity provider values into ElevenLabs:\n\n * Use the **Microsoft Entra Identifier** for **Identity Provider Entity Id**.\n * Use the **Login URL** for **Identity Provider Sign-In URL**.\n\n <Frame background=https://elevenlabs.io/"subtle/">/n <img src=https://elevenlabs.io/"file:assets/images/entra-saml-idp-values.png/" alt=\"Microsoft Entra set up values showing Login URL and Microsoft Entra Identifier\" />\n </Frame>\n </Step>\n\n <Step title=\"Add your allowed email domain\">\n In ElevenLabs, click **Add Domain** and select the verified domain that matches the email domain\n of your Microsoft Entra users.\n\n <Frame background=https://elevenlabs.io/"subtle/">/n <img src=https://elevenlabs.io/"file:assets/images/entra-saml-add-domain.png/" alt=\"ElevenLabs Add allowed email domains dialog\" />\n </Frame>\n </Step>\n\n <Step title=\"Save the SSO provider\">\n Review the configuration, select **I acknowledge this change will log out users currently using\n SSO**, then click **Update SSO**.\n </Step>\n</Steps>\n\n## Field mappings\n\nUse this table to map Microsoft Entra SAML settings to ElevenLabs SSO fields.\n\n| Microsoft Entra field or location | ElevenLabs field | Value to use |\n| ---------------------------------------------- | --------------------------------- | ----------------------------------------------------------------------------------------- |\n| **Sign-in method** | **SSO Provider** | `SAML` |\n| **Identifier (Entity ID)** | **Service Provider Entity Id** | Use the ElevenLabs value, for example `https://elevenlabs.io` |\n| **Reply URL (Assertion Consumer Service URL)** | **Redirect URL** | Use the ElevenLabs value, for example `https://elevenlabs.io/__/auth/handler` |\n| **Microsoft Entra Identifier** | **Identity Provider Entity Id** | Entra issuer, for example `https://sts.windows.net/{tenant-id}/` |\n| **Login URL** | **Identity Provider Sign-In URL** | Entra SAML sign-in URL, for example `https://login.microsoftonline.com/{tenant-id}/saml2` |\n| **Certificate (Base64)** | **Certificate** | Entra token signing certificate in valid PEM format |\n| **Name ID format** | No manual config required | Set to **Email address** |\n| **Name ID source attribute** | No manual config required | Field containing the user's email, usually `user.mail` (or `user.userprincipalname`) |\n| User or app email domain in Microsoft Entra | **Domain** | Must match a verified ElevenLabs domain, for example `company.com` |\n\n## Troubleshooting\n\n<AccordionGroup>\n <Accordion title=\"Microsoft Entra shows a successful sign-in, but ElevenLabs says unable to sign in\">\n Check the browser Network response for `accounts:signInWithIdp`. Microsoft Entra sign-in logs only\n confirm that Entra authenticated the user. ElevenLabs can still reject the SAML response if the\n assertion values do not match the SSO configuration.\n </Accordion>\n\n <Accordion title=\"INVALID_IDP_RESPONSE: Error when parsing certificate\">\n The browser Network response may show `INVALID_IDP_RESPONSE: Error when parsing certificate`.\n Remove the certificate from ElevenLabs, then re-add the Entra **Certificate (Base64)** in valid\n PEM format. Do not use an LLM to format the certificate. Open the Base64 certificate in a text\n editor and copy it exactly, including `-----BEGIN CERTIFICATE-----` and\n `-----END CERTIFICATE-----`.\n </Accordion>\n\n <Accordion title=\"Unable to login with saml.workspace... or user mismatch errors\">\n Make sure Microsoft Entra sends the user's email address as the `NameID`. In **Attributes &\n Claims**, set the **Unique User Identifier (Name ID)** claim **Name identifier format** to **Email\n address** and **Source attribute** to the field that contains the email address for all users\n (usually `user.mail`, or `user.userprincipalname` if `user.mail` is not populated). Inside the\n `<saml:Subject>` field of the SAML response, `<saml:NameID>` must be the user's email address.\n </Accordion>\n\n <Accordion title=\"Which Microsoft Entra values should I use?\">\n Use the **Microsoft Entra Identifier** for **Identity Provider Entity Id**, the **Login URL** for\n **Identity Provider Sign-In URL**, and the **Certificate (Base64)** for **Certificate**.\n </Accordion>\n</AccordionGroup>\n"],"perViewerCopy":[0,true],"askAiEnabled":[0,false],"skillsConfig":[0],"availability":[0],"pageActions":[0,{"options":[0,{"copyPage":[0,true],"viewAsMarkdown":[0,true],"askAi":[0,true],"openAi":[0,true],"claude":[0,true],"cursor":[0,true],"claudeCode":[0,true],"vscode":[0,false],"custom":[1,[[0,{"title":[0,"LLMs full"],"subtitle":[0,"See the entire documentation site as markdown for LLMs"],"url":[0,"https://elevenlabs.io/docs/llms-full.txt"],"icon":[0,"fa-solid fa-file-code"]}]]]}]}],"pageActionsStyle":[0,"default"],"pageActionFiles":[0],"showRssFeedButton":[0,false],"showPageActions":[0,true]}" ssr client="deferred" opts="{"name":"PageHeaderIsland","value":true}" await-children>

Microsoft Entra SAML SSO

Configure Microsoft Entra ID as a SAML identity provider for ElevenLabs SSO.

Microsoft Entra SAML SSO lets workspace members sign in to ElevenLabs through a Microsoft Entra ID (formerly Azure AD) enterprise application.

SSO is available for Enterprise workspaces. Only Workspace admins can configure SSO settings.

ElevenLabs supports Service Provider (SP) initiated SAML SSO. To start sign-in, use https://elevenlabs.io/app/sign-in?use_sso=true. You can add email=user@example.com as a query parameter to prefill the email field.

Microsoft Entra is only supported through SAML. OIDC with Microsoft Entra is not recommended and can cause sign-in issues.

Prerequisites

  • An Enterprise ElevenLabs workspace.
  • Workspace admin access in ElevenLabs.
  • Admin access in the Microsoft Entra admin center.
  • A verified email domain in ElevenLabs for the users who will sign in through Microsoft Entra.

Set up Microsoft Entra SAML SSO

1

Open SSO settings in ElevenLabs

Go to Workspace settings > Security & SSO.

2

Verify your email domain

Under User Auto Provisioning, verify the email domain your Microsoft Entra users will sign in with. Enter the domain (subdomains are allowed), then follow the prompts to confirm ownership. Optionally enable auto-provisioning so users with a matching email domain automatically join your workspace.
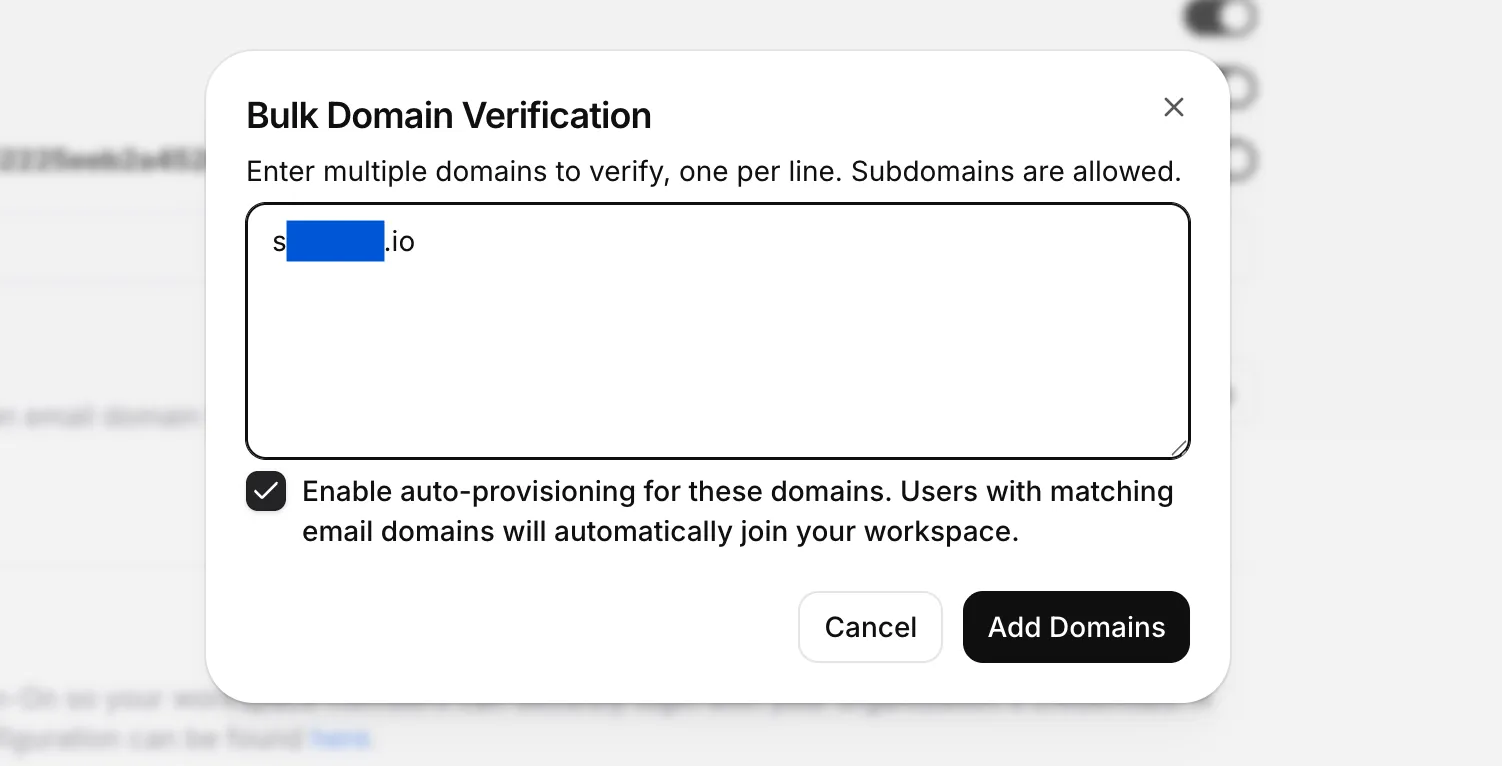
ElevenLabs bulk domain verification dialog
4

Select SAML as the SSO provider

In SSO Provider, select SAML. Copy the Service Provider Entity Id and Redirect URL values. You will use these values in Microsoft Entra.

5

Create a Microsoft Entra enterprise application

In the Microsoft Entra admin center, open your directory Overview, then click Add > Enterprise application.
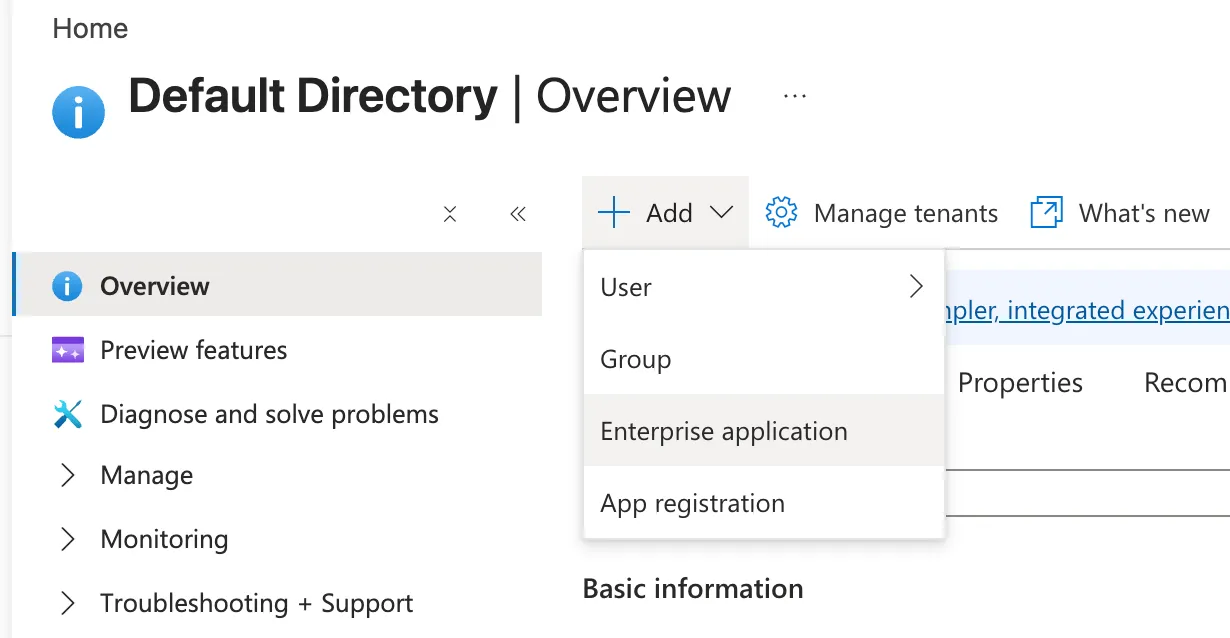
Microsoft Entra Overview Add menu with Enterprise application selected

On Browse Microsoft Entra App Gallery, click Create your own application.
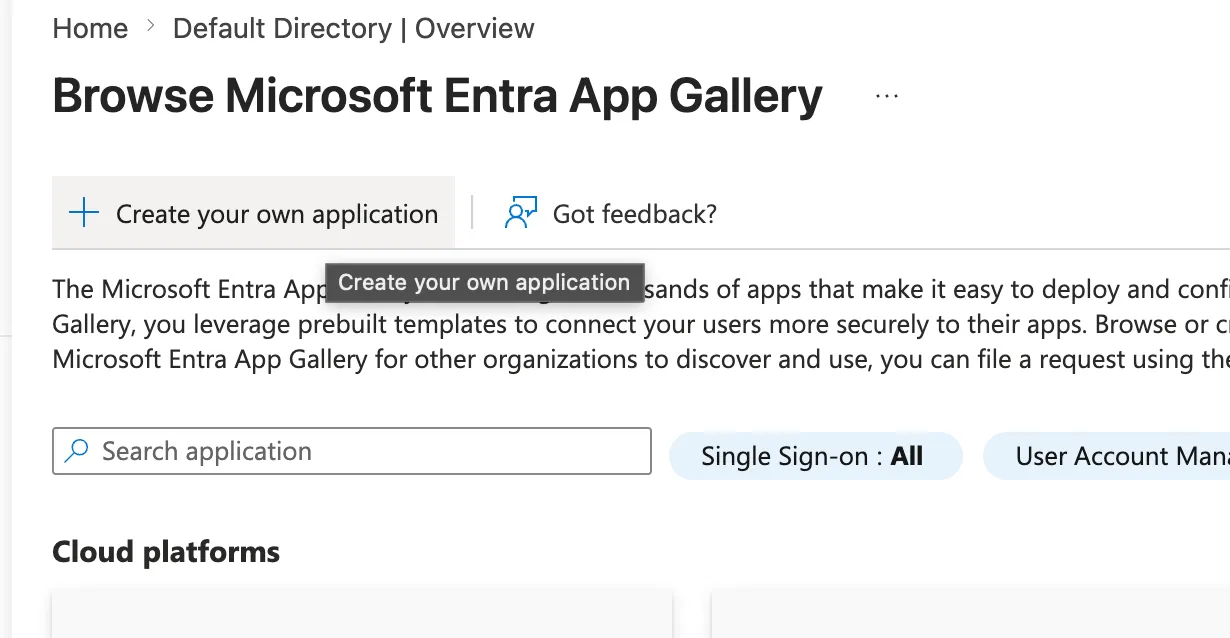
Microsoft Entra App Gallery with Create your own application
6

Name the application

Enter a name (for example, ElevenLabs), select Integrate any other application you don’t find in the gallery (Non-gallery), then click Create.
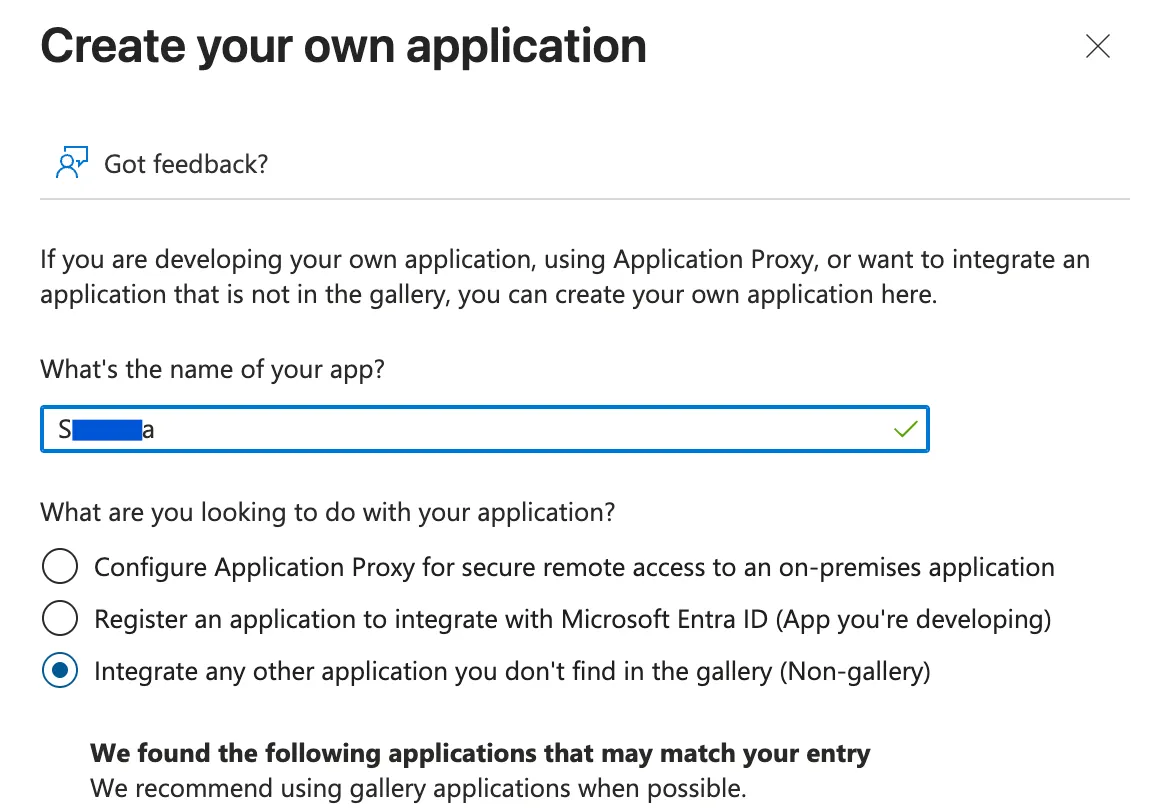
Microsoft Entra Create your own application panel with a non-gallery app
7

Start single sign-on setup

On the application Overview, under Getting Started, select Set up single sign on > Get started.
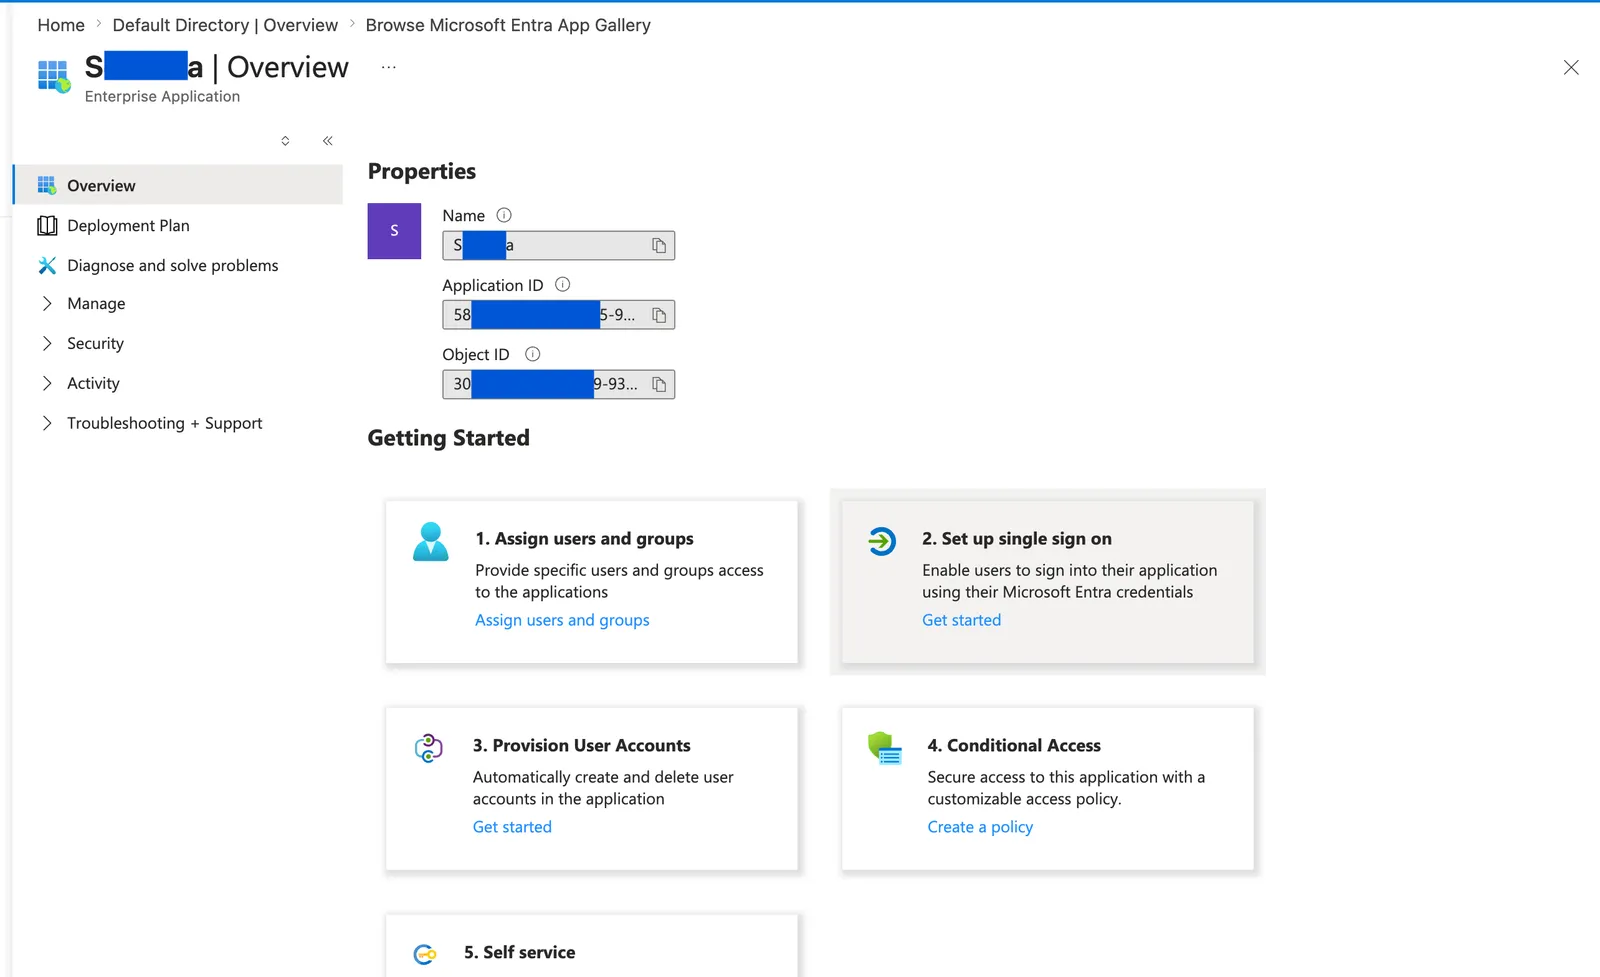
Microsoft Entra enterprise application Getting Started with Set up single sign on

Select SAML as the single sign-on method.
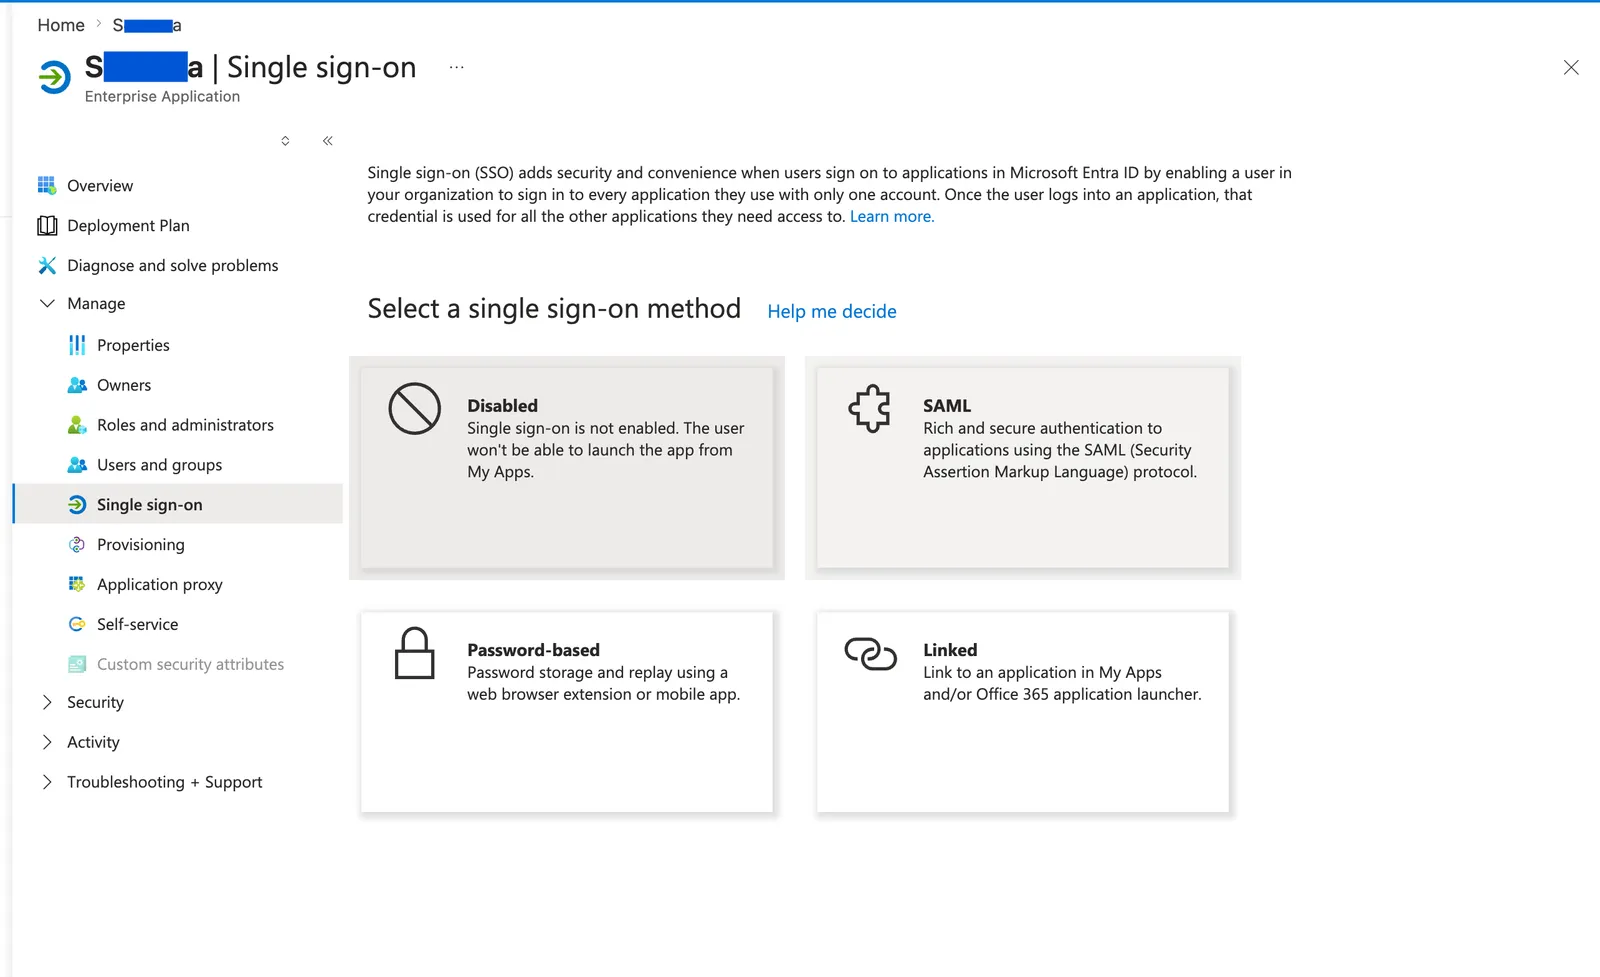
Microsoft Entra Select a single sign-on method with SAML
8

Configure basic SAML settings

In Basic SAML Configuration, configure the app with the values from ElevenLabs:

  • Set Identifier (Entity ID) to the ElevenLabs Service Provider Entity Id.
  • Set Reply URL (Assertion Consumer Service URL) to the ElevenLabs Redirect URL.
  • Leave Sign on URL blank. ElevenLabs uses SP-initiated SSO.

Click Save.
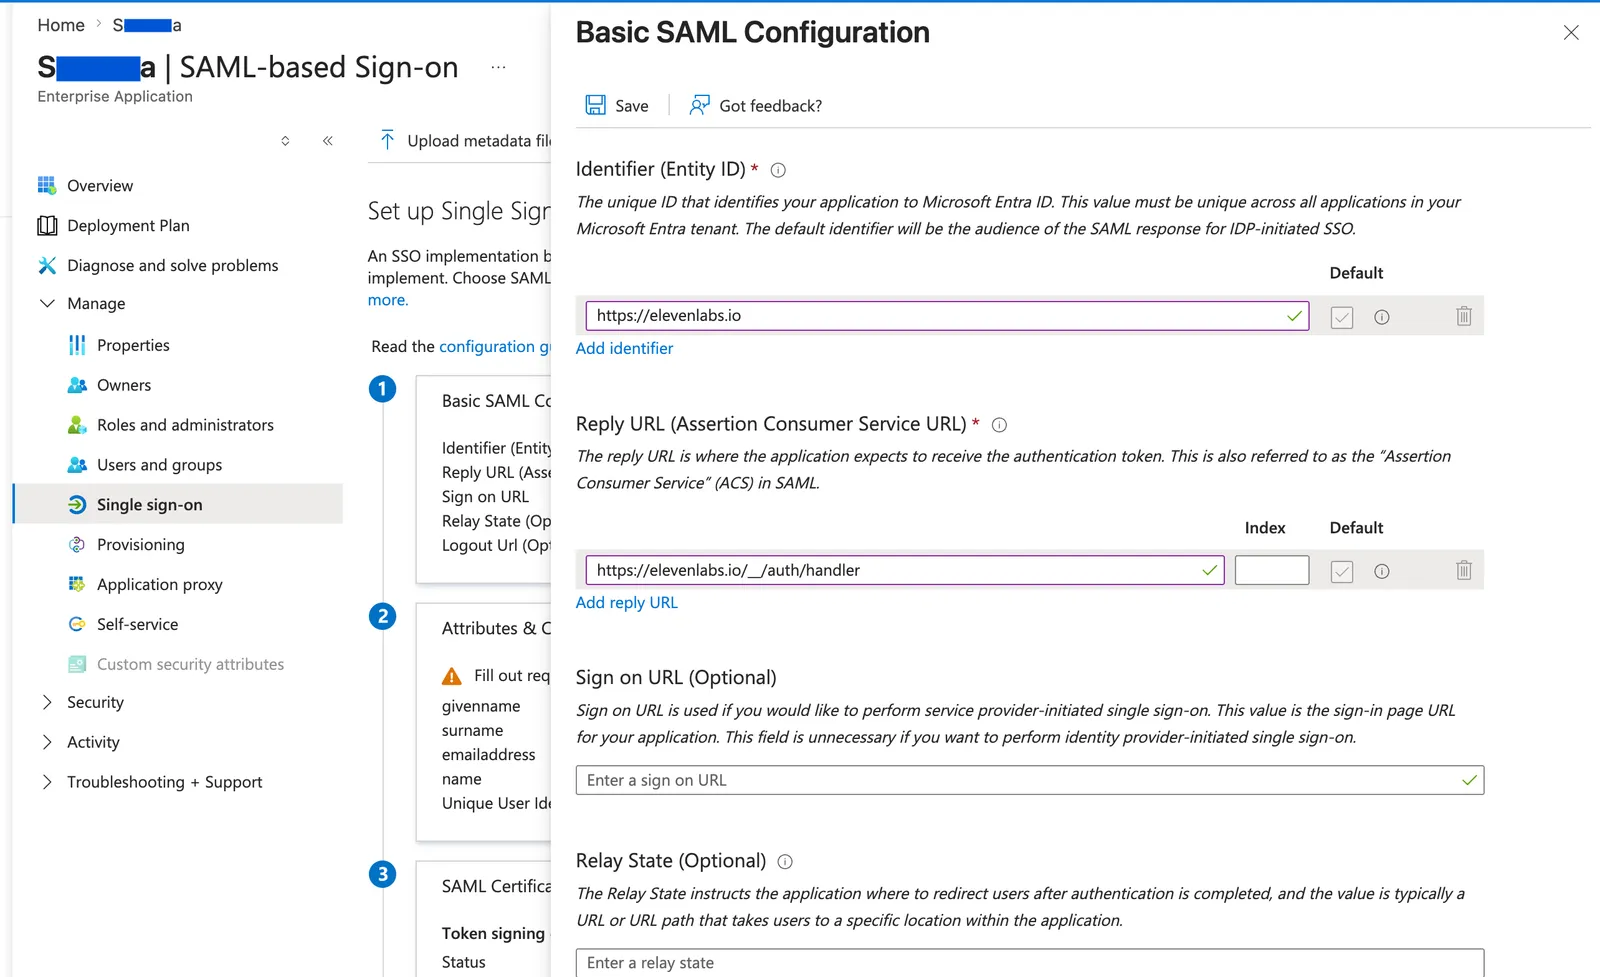
Microsoft Entra Basic SAML Configuration with Identifier and Reply URL

For data residency environments, use https://<region>.residency.elevenlabs.io/__/auth/handler as the Reply URL, replacing <region> with your region code.

9

Configure the Name ID claim

In Attributes & Claims, edit the Unique User Identifier (Name ID) claim:

  • Set Name identifier format to Email address.
  • Set Source to Attribute.
  • Set Source attribute to the field that contains the email address for all users. This is usually user.mail, but may be user.userprincipalname.

Click Save.

Choose the attribute that holds an email address for every user. If user.mail is not populated for all of your users, use user.userprincipalname instead.
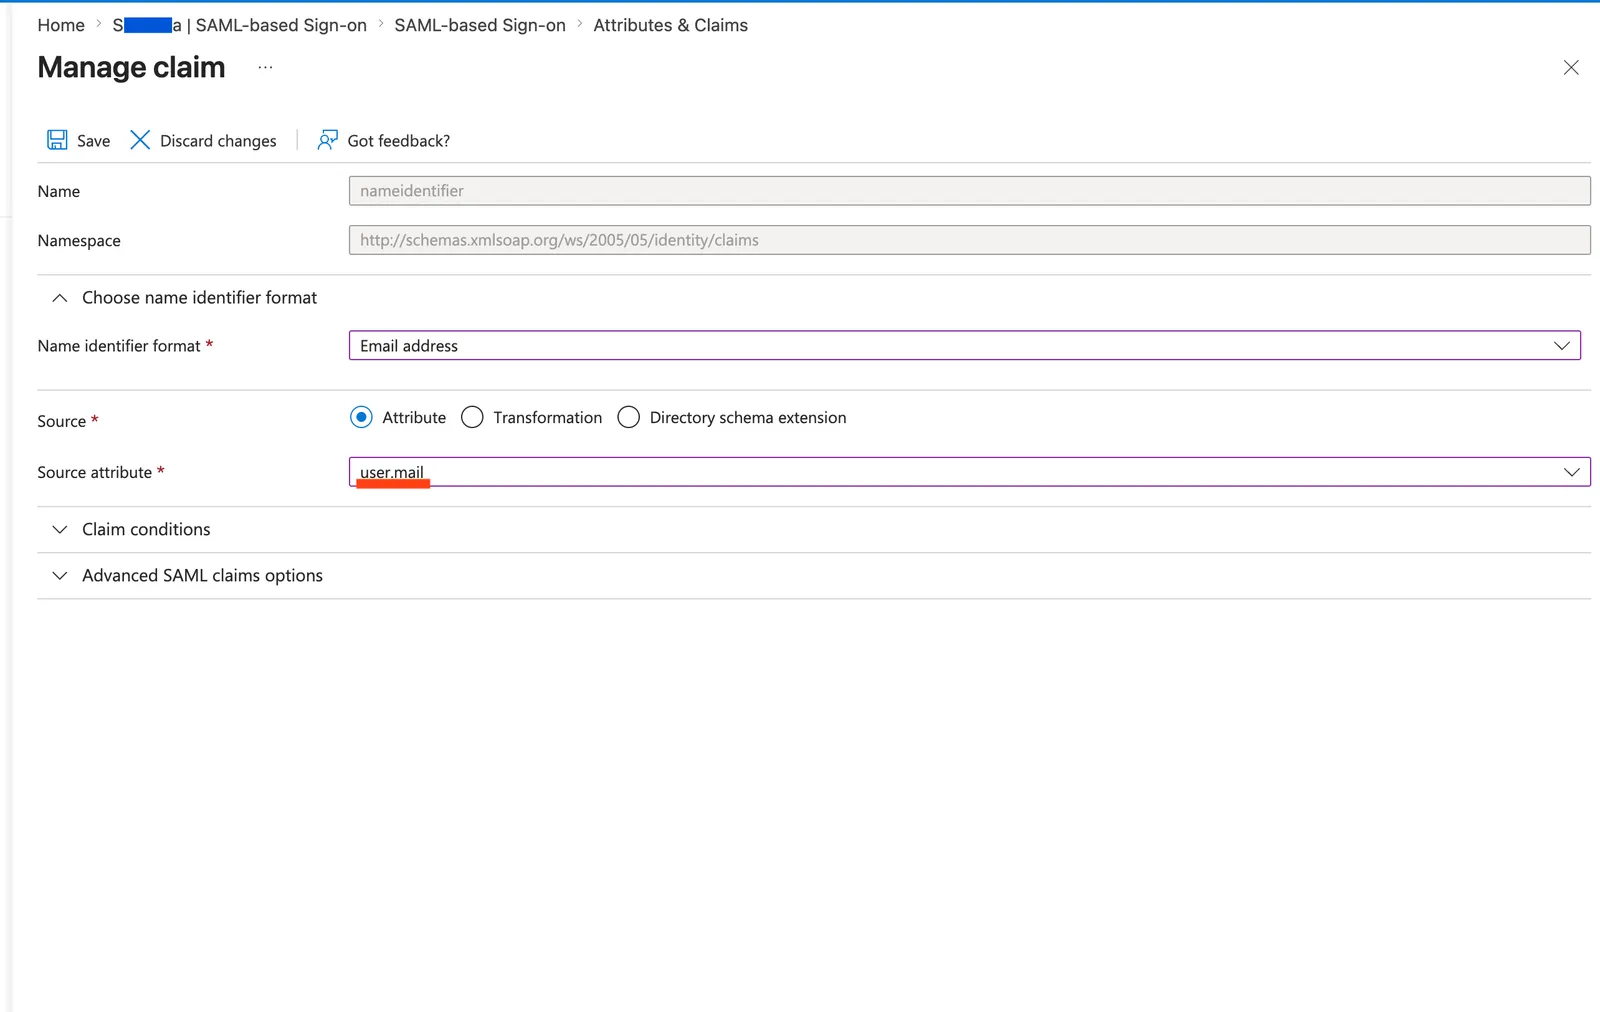
Microsoft Entra Manage claim with Email address format and user.mail source attribute
10

Download the signing certificate

In SAML Certificates, next to Certificate (Base64), click Download. Open the downloaded file in a text editor.
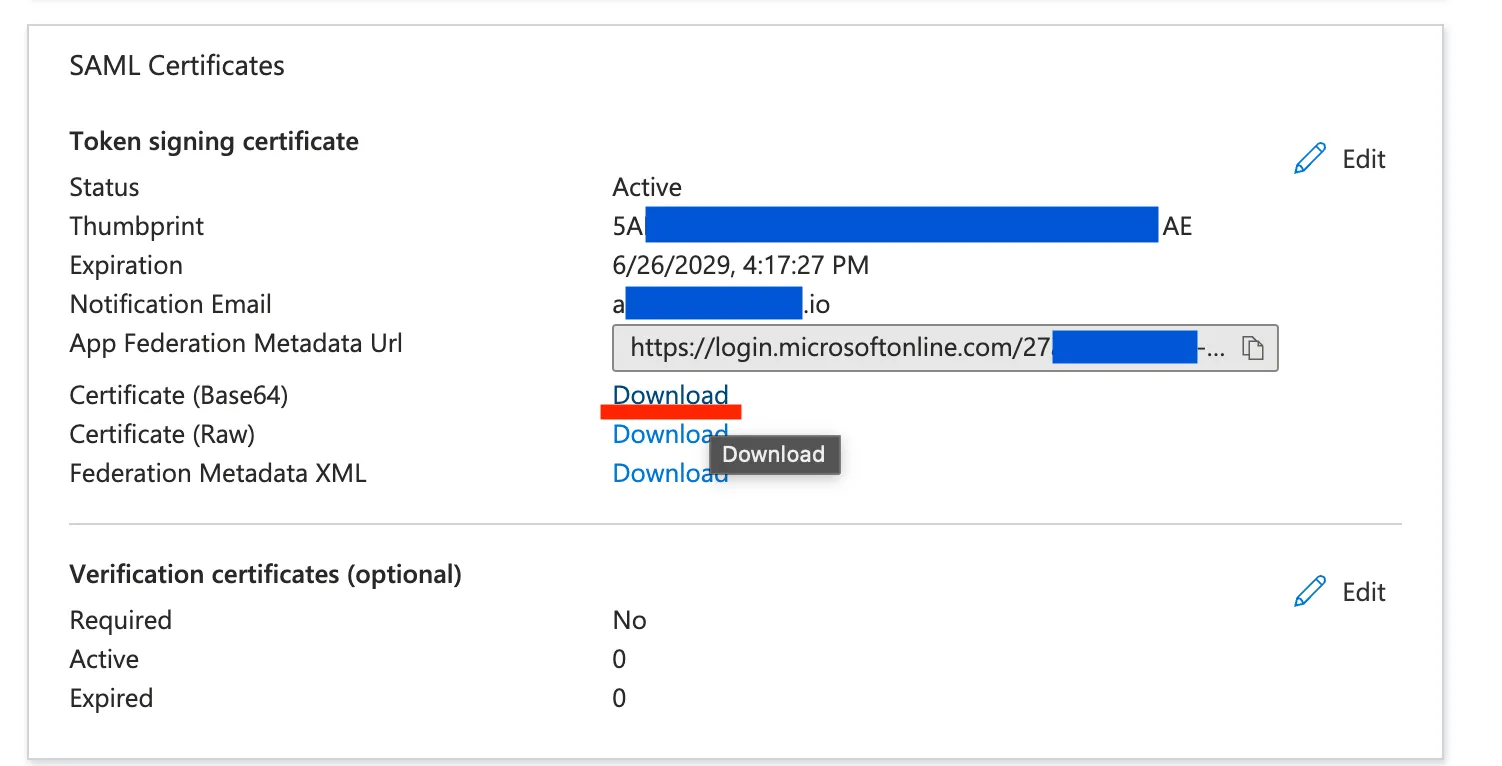
Microsoft Entra SAML Certificates with Certificate Base64 download
11

Assign users or groups

Open the app’s Users and groups, then assign the users or groups that should be able to sign in to ElevenLabs.
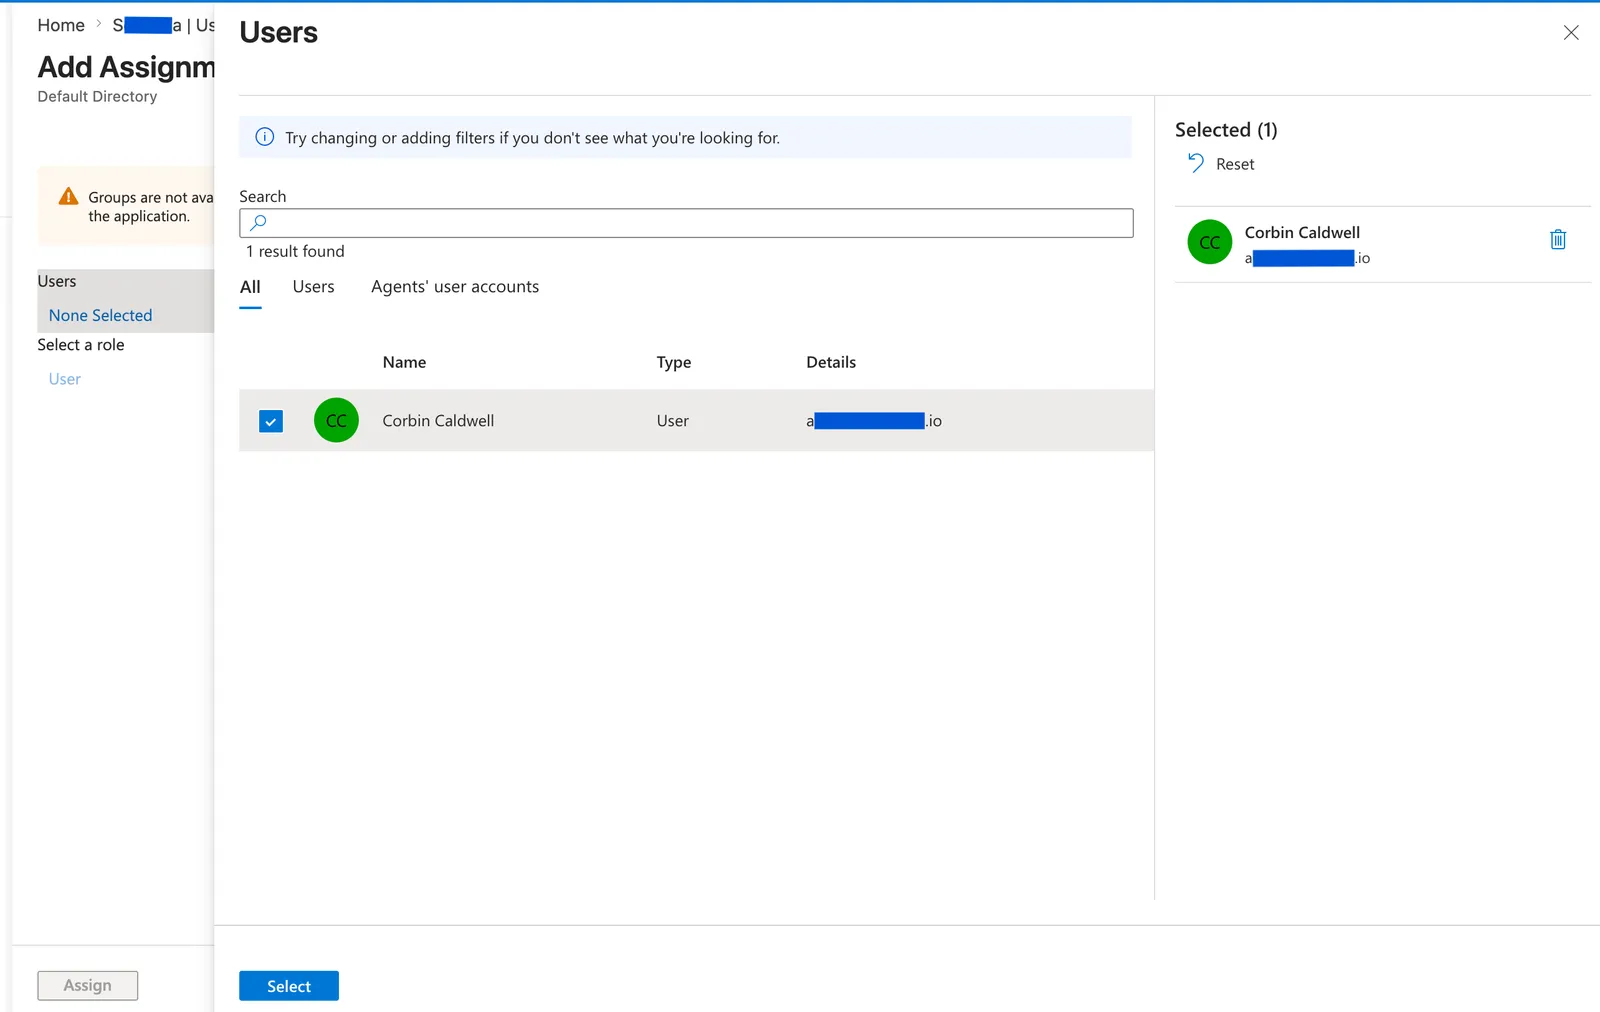
Microsoft Entra Add Assignment users list
12

Add the Entra certificate to ElevenLabs

In ElevenLabs, click Add Certificate. Paste the full PEM certificate from the Base64 file, including -----BEGIN CERTIFICATE----- and -----END CERTIFICATE-----, then click Add.
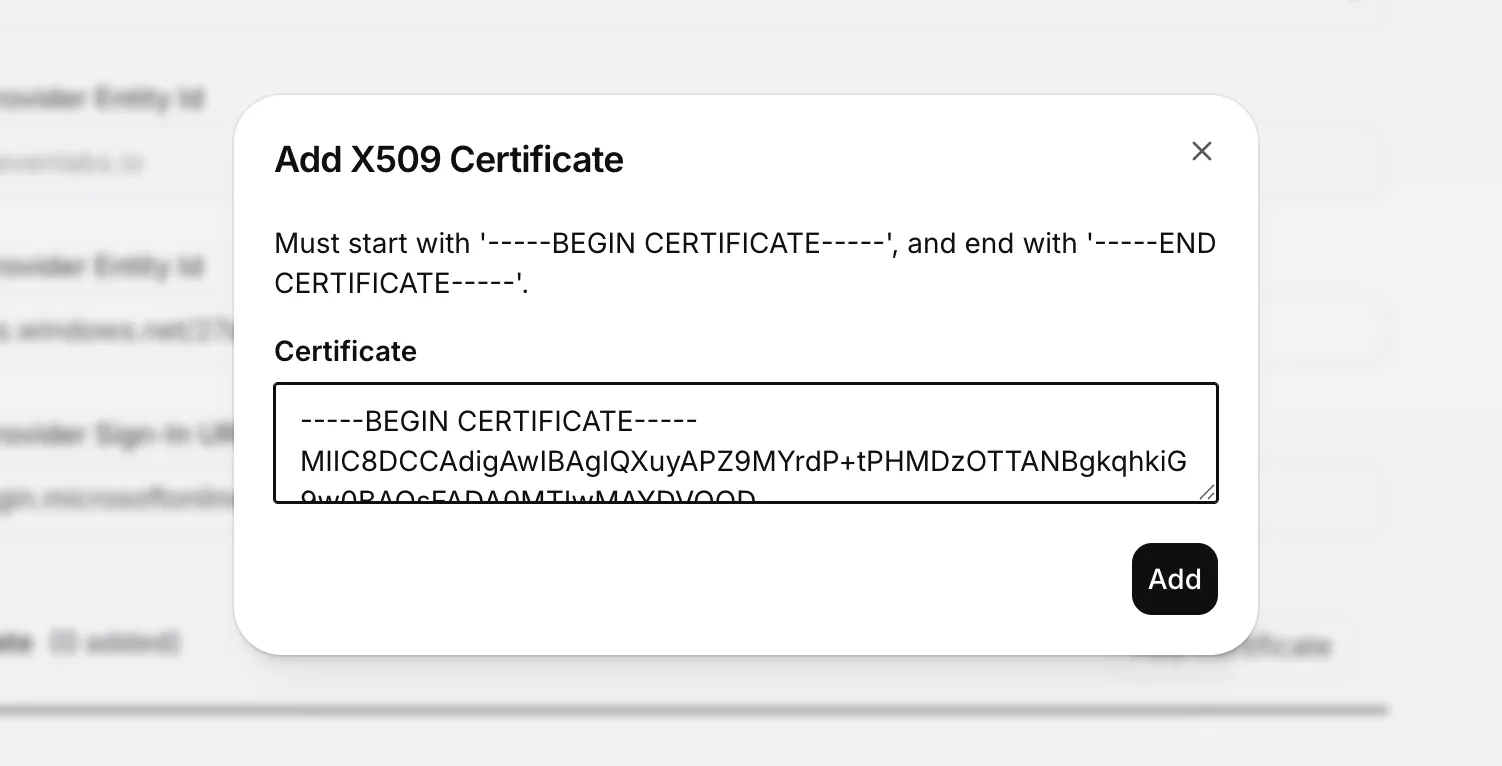
ElevenLabs Add X509 Certificate dialog
13

Copy Entra identity provider values into ElevenLabs

In the Microsoft Entra Set up section, copy the identity provider values into ElevenLabs:

  • Use the Microsoft Entra Identifier for Identity Provider Entity Id.
  • Use the Login URL for Identity Provider Sign-In URL.
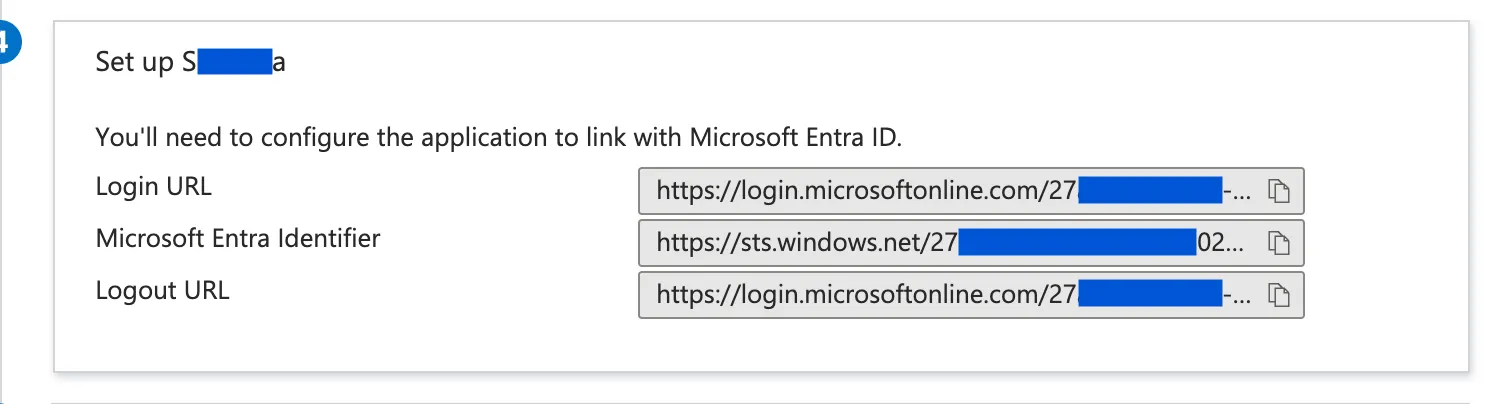
Microsoft Entra set up values showing Login URL and Microsoft Entra Identifier
14

Add your allowed email domain

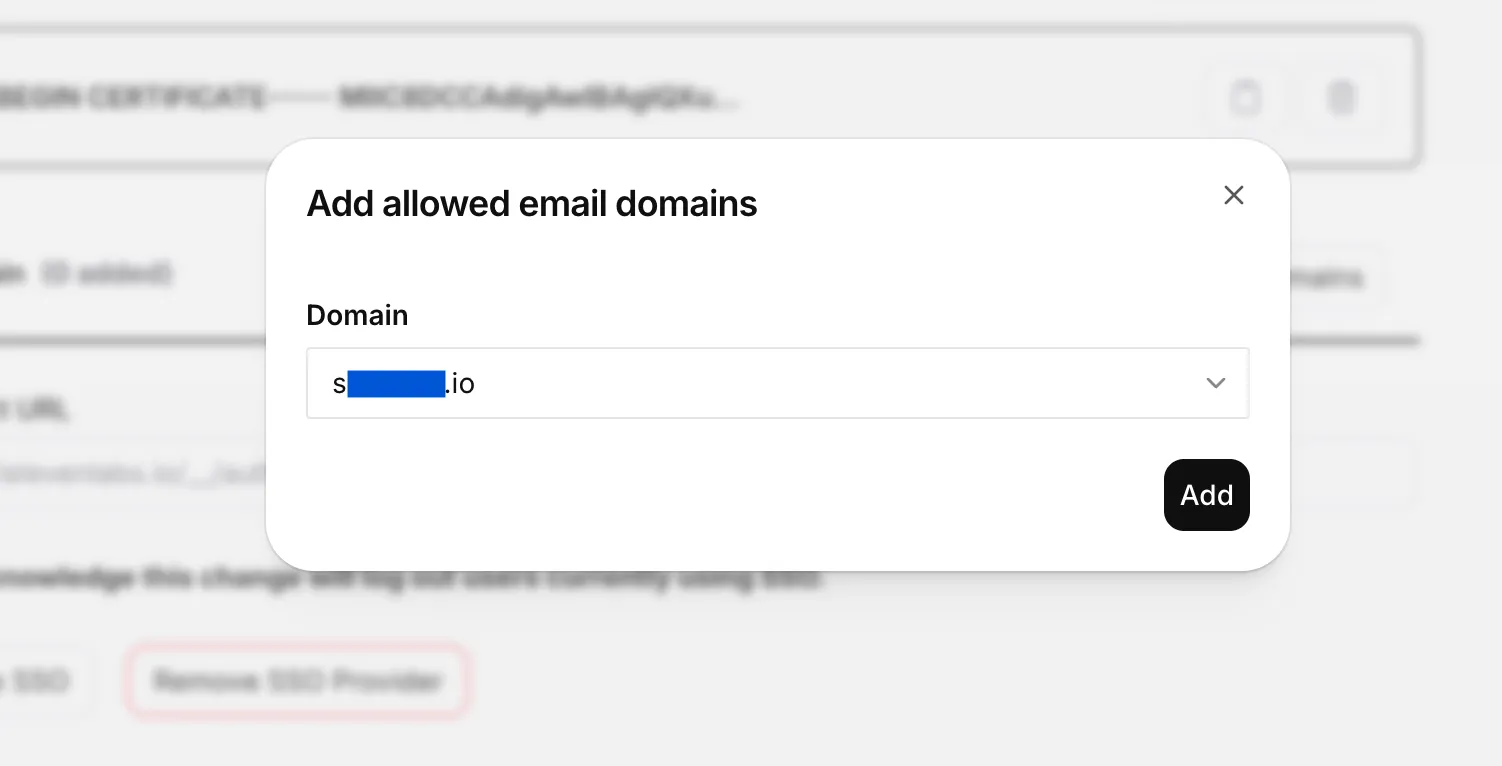
In ElevenLabs, click Add Domain and select the verified domain that matches the email domain of your Microsoft Entra users.

ElevenLabs Add allowed email domains dialog
15

Save the SSO provider

Review the configuration, select I acknowledge this change will log out users currently using SSO, then click Update SSO.

Field mappings

Use this table to map Microsoft Entra SAML settings to ElevenLabs SSO fields.

Microsoft Entra field or locationElevenLabs fieldValue to use
Sign-in methodSSO ProviderSAML
Identifier (Entity ID)Service Provider Entity IdUse the ElevenLabs value, for example https://elevenlabs.io
Reply URL (Assertion Consumer Service URL)Redirect URLUse the ElevenLabs value, for example https://elevenlabs.io/__/auth/handler
Microsoft Entra IdentifierIdentity Provider Entity IdEntra issuer, for example https://sts.windows.net/{tenant-id}/
Login URLIdentity Provider Sign-In URLEntra SAML sign-in URL, for example https://login.microsoftonline.com/{tenant-id}/saml2
Certificate (Base64)CertificateEntra token signing certificate in valid PEM format
Name ID formatNo manual config requiredSet to Email address
Name ID source attributeNo manual config requiredField containing the user’s email, usually user.mail (or user.userprincipalname)
User or app email domain in Microsoft EntraDomainMust match a verified ElevenLabs domain, for example company.com

Troubleshooting

Check the browser Network response for accounts:signInWithIdp. Microsoft Entra sign-in logs only confirm that Entra authenticated the user. ElevenLabs can still reject the SAML response if the assertion values do not match the SSO configuration.

The browser Network response may show INVALID_IDP_RESPONSE: Error when parsing certificate. Remove the certificate from ElevenLabs, then re-add the Entra Certificate (Base64) in valid PEM format. Do not use an LLM to format the certificate. Open the Base64 certificate in a text editor and copy it exactly, including -----BEGIN CERTIFICATE----- and -----END CERTIFICATE-----.

Make sure Microsoft Entra sends the user’s email address as the NameID. In Attributes & Claims, set the Unique User Identifier (Name ID) claim Name identifier format to Email address and Source attribute to the field that contains the email address for all users (usually user.mail, or user.userprincipalname if user.mail is not populated). Inside the <saml:Subject> field of the SAML response, <saml:NameID> must be the user’s email address.

Use the Microsoft Entra Identifier for Identity Provider Entity Id, the Login URL for Identity Provider Sign-In URL, and the Certificate (Base64) for Certificate.